Blog
-
Nobody at USDA Asked About the Firewall
Archer Daniels Midland is mostly out of the False Claims Act woods, and the story of how it got there is the most useful ruling on cyber-FCA enforcement in years. Nobody sued. Nobody settled. The relator, Mark Pannek, lost on paper, in a memorandum and order from Judge Sanjay Harjani of the Northern District of…

-
The CMMC Pause Isn’t a Holiday
This week, two things happened involving the same federal document. On September 9, Washington Technology reported that the Cybersecurity Maturity Model Certification (CMMC) Phase 2 suspension had been “locked in with binding regulation,” a step change from a mere pause that would make reversal harder. The same week, the analysts at RedSpin compared the new…
-
Four Years, Fourteen Lawsuits, $136 Million in Revenue: what OneTouchPoint’s ransomware bill actually added up to
On November 18, 2026, a Wisconsin state judge in Waukesha County will convene a final approval hearing for a class action settlement arising from a ransomware attack that began on April 27, 2022. Four years, six months, and a courtroom transfer separate the two dates, along with fourteen lawsuits, three failed mediations, a partially successful…
-
The EU CRA Reporting Deadline Is Friday. Here’s What US Manufacturers Actually Need to Do.
If you build software or hardware with digital elements and you sell it into Europe, the EU Cyber Resilience Act (CRA) stops being a someday problem this Friday, September 11. That’s when the regulation’s reporting obligations start. It’s not a registration deadline and not a paperwork deadline. It’s the moment the duty to notify regulators…
-
The Ransom Was the Cheap Part
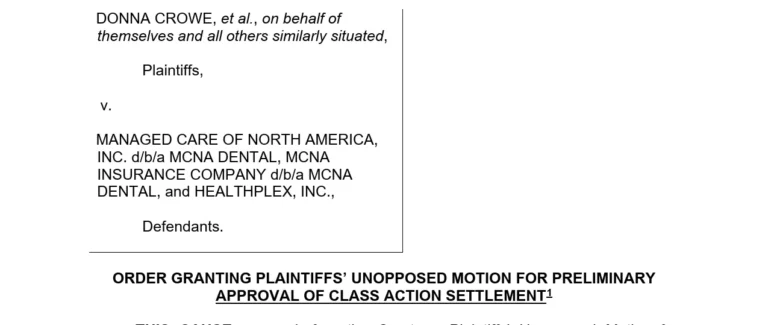
In March 2023, LockBit demanded $10 million from MCNA Dental. Management refused, the attackers published 700 GB of stolen data two days later, and everyone moved on. That refusal tends to get framed as courage in breach retrospectives. It wasn’t. It was a capital allocation decision made without anyone pricing the alternatives, and the invoice…
-
Honeywell Paid $2 Million to Make a Quantum Problem Go Quiet
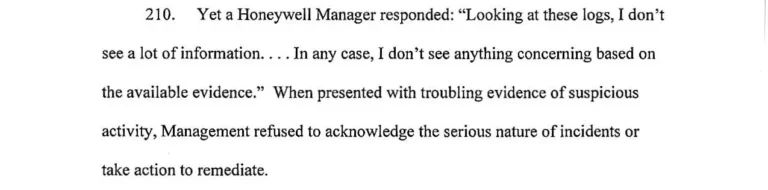
On December 14, 2020, one day after the SolarWinds breach became public knowledge, monitoring software on a Honeywell network started firing alerts. Between 9:30 in the morning and midnight Central Time, it logged: A manager looked at the logs and concluded, “I don’t see anything concerning based on the available evidence.” The three-hour session with…
-
How to Build a Business Case for Cybersecurity Investments
In August 2026, California’s Department of Financial Protection and Innovation (DFPI) ordered Academy Mortgage to pay $825,000 for failing to protect the personal information of 284,443 people. That penalty was the smallest line on a much larger invoice. My estimate, built from IBM’s 2026 Cost of a Data Breach benchmarks scaled to Academy’s size, puts…
-
What the AI Kill Switch Act Actually Switches Off
Two things landed this week that got me checking back in on H.R. 9917, the AI Kill Switch Act that Reps. Ted Lieu and Nathaniel Moran introduced on July 23. The first was a CyberScoop op-ed arguing the bill repeats the Clipper Chip’s mistakes. The second was a PBS NewsHour segment I’d watched on AI…
-
The Best Data Is on Sale at the Liquidation Auction
The final round of bidding for the internal records of a dead airline came down to two companies. Google offered $10 million, and the runner-up, at $7.5 million, was Mercor, an AI training-data firm. Neither company flies planes, runs turnaround operations, or collects archives. Both train AI models. That auction happened on August 14 in…
-
Washington’s Privacy Gap Has a Map Now
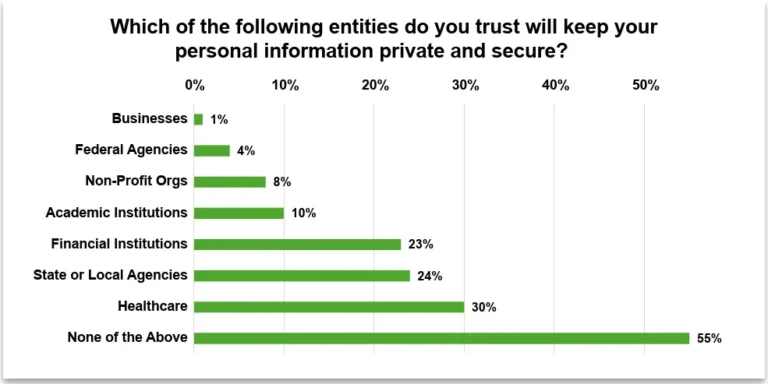
Washington is home to Amazon, Microsoft, and one of the most data-dependent economies in the country. It doesn’t have a generally applicable consumer privacy law. Three attempts at one failed in 2019, 2020, and 2021, and each time the cause it failed was the same fight: the Senate wanted Attorney General-only enforcement, the House wanted…