A Colorado Judge Just Explained Why Restrictive AI Policies Backfire
A recent discovery ruling in Colorado is the clearest argument I’ve seen for why restrictive AI policies fail, and what to do instead.
On August 31, 2026, a magistrate judge in Colorado resolved a routine-looking discovery fight and, in doing so, handed corporate America a free lesson in AI governance. The case was Dunn v. LexisNexis Risk Solutions, Inc., and the disputed material sat under the heading “Additional Disputed Language,” which sounds innocuous enough. It wasn’t. The fight was over whether a party using a new AI tool during litigation had to obtain its opponent’s written consent and then formally amend the protective order before touching the tool.
Read the full order by Magistrate Judge Maritza Dominguez Braswell, (No. 26-cv-01249-GPG-MDB) and you’ll notice she didn’t reject the requirement because AI tools are harmless. She rejected it because the parties had already agreed to the protections that actually matter, and the leftover language was pure process theater.
“The parties are capable of evaluating whether a new tool satisfies the standing requirements.”
That sentence is the entire ruling in miniature, and it happens to be the entire thesis of sane AI governance.
What the Parties Already Agreed To
The Surviving Protections
Before anyone fought about anything, the litigants had negotiated an AI provision with real teeth. Under the agreed language, neither side could:
- Feed protected material into models for training purposes
- Share it with third parties beyond what was needed to deliver the service
- Walk away from deletion obligations
Both sides also identified the specific tools they planned to use up front. Then the defense asked for more.
The Rejected Language
That “more” was a consent-and-amend requirement, the litigation equivalent of a change control board staffed by opposing counsel. Every time either party wanted to try a new tool, it would need signoff, and if signoff didn’t come voluntarily, a trip back to federal court. Judge Braswell didn’t see the utility in that process, noting the agreed provision already set tool-agnostic requirements durable enough to survive new vendors entering the market.
| What Survived | What She Cut |
|---|---|
| No training on protected material | Mandatory opponent consent per new tool |
| Deletion obligations | Protective order amendments |
| Identified tools at signing | Motion practice when consent didn’t come |
Substance over ceremony, decided in one order instead of a dozen motions.
Why Gatekeeping Backfires Outside the Courthouse Too
If you run security or IT for a living, you already know what happens when the approved path is slower than the unapproved one. People route around you, and they always have, whether the detour was USB drives slipped into a jacket pocket or a SaaS (software-as-a-service) subscription bought on a department credit card. Generative AI just handed them a faster escape hatch than both eras combined.
The mistake executives make is assuming shadow AI is a discipline problem. It isn’t. Employees who paste a contract into a consumer chatbot at 6PM to meet a deadline aren’t malicious; they’re solving the immediate problem in front of them with the tools within reach. When your intake process for a new AI tool takes four weeks and a committee that meets quarterly, you haven’t reduced organizational AI use. You’ve reduced your visibility into it.
A Chief Information Security Officer (CISO) who claims the org runs no unapproved AI is describing their monitoring coverage, not their employees’ behavior.
Restriction without accessibility doesn’t shrink the risk surface. It relocates it somewhere you can’t see, which is the worst possible trade in security.
The Outcomes Are Public Now
For a while, shadow AI consequences lived in the land of the hypothetical. Not anymore.
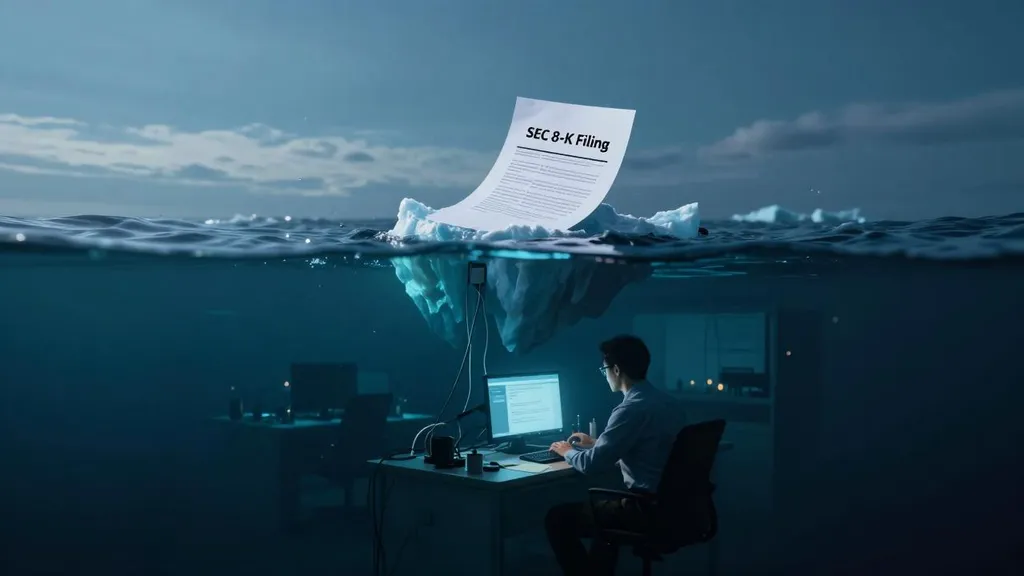
In late 2025, Community Bank learned that an employee had pasted customer information, including names, birthdates, and Social Security numbers, into an unauthorized external AI tool. The exposure was serious enough to require a Form 8-K filing with the Securities and Exchange Commission (SEC), which put the incident on the public record. Somewhere between the first approval request that went nowhere and the moment a reg filing got drafted, the bank lost control of the narrative. Nobody files an 8-K over an experiment that was approved and logged.
That damage compounds too:
- Confidential business information disclosed to consumer-grade tools sits outside the contractual protections your lawyers negotiated
- Trade secrets can lose their protected status once they leak into a service with no enterprise terms
- Unverified output from a rushed prompt (AKA “slop”) gets pasted into deliverables nobody upstream checks
What Substantive Guardrails Look Like
Here’s the part Judge Braswell got right, translated out of litigation and into enterprise policy. The protective order that survived her scrutiny didn’t list approved vendors. It set criteria any competent professional could apply to a new tool independently, and your acceptable use policy (AUP) should do the same.
Four criteria do most of the work:
- Training controls. Can the provider train on your inputs, and can that setting be locked off contractually rather than toggled hopefully?
- Data handling. Where does input go, who are the subprocessors, what survives retention and deletion windows, and can you actually enforce deletion?
- Security posture. Independent audit evidence, like SOC 2 Type II and ISO 27001 at a minimum for anything touching regulated data.
- Tiering. Consumer accounts for public information, enterprise agreements with real terms for everything else, and a published matrix so employees self-select the right tier without opening a ticket.
None of that requires a human in the loop for every new tool. It requires publishing standards a reasonable employee can follow.
The Policy That Works Is the One People Use
Every shadow AI incident I’ve seen traced back to the same root cause, and it was never employees trying to do something malicious. It was an approved path designed for a world where software arrived quarterly, procurement was the only buyer, and experimentation required a budget line. People who need an answer today won’t wait for a committee that meets Tuesday after next.
Notice what’s absent. Nowhere does it say “make employees beg permission to test a summarization tool on a non-sensitive document.” Approval cycles exist for material risk, not as punishment for curiosity.
So the measure of a good AI policy isn’t how restrictive it reads in the PDF. It’s whether the sanctioned enterprise tool is good enough, accessible enough, and fast enough that using it is the path of least resistance. Publish the criteria. Provision the tool. Log the usage. And make the reporting channel for “I pasted something into the wrong window” one that doesn’t end careers, because you want that call before the incident becomes an 8-K, not after.
The Colorado court trusted competent professionals to apply clear standards without a chaperone. That’s not a naive bet on human nature. It’s what AI governance looks like when it works, and it’s a cheaper lesson than learning it from a filing with the SEC or buying some vendor’s shiny tool without the basic processes in place first.