The Price Tag On Safe Fleet’s Data Breach
When someone steals personnel files on 7,478 current and former employees, the invoice doesn’t arrive all at once. It dribbles in over two and a half years, disguised as legal fees, settlement payouts, credit monitoring subscriptions, and administrator invoices. Safe Fleet Holdings, the Missouri-based fleet safety manufacturer that Oak Hill Capital sold to Clarience Technologies in February 2024, is now finding that out in public, one line item at a time.
There’s no such thing as cyber risk. There’s business risk that occasionally involves computers, and this case is a clean example. Somewhere in the Safe Fleet hierarchy, somebody accepted a risk, consciously or not, and the cost of that acceptance is now calculable. What follows is a reconstruction of what this breach cost the company, alongside what it would have cost to prevent.
The Breach Timeline
On or before April 13, 2024, an unauthorized party accessed Safe Fleet’s systems and took personnel data belonging to 7,478 people. The data haul included names, addresses, dates of birth, Social Security numbers (SSNs), driver’s license information, passport details, taxpayer IDs, financial account numbers, payment cards, usernames and passwords, plus health insurance and medical information. Whoever got in didn’t grab customer records. They grabbed HR’s file cabinet.
Nobody noticed for 409 days, until an outside cybersecurity firm, brought in to investigate suspicious activity, found the intrusion on May 27, 2025. Written notification to affected individuals went out July 18, 2025, which put the gap between breach and notification at 461 days. Missouri’s notification statute requires disclosure “without unreasonable delay.” A 15-month tour of the statute apparently didn’t raise the urgency.
The breach was too small to earn tech press coverage, so it flew under the radar. Then the lawyers arrived. Named plaintiffs Brian Ferry and David Clement filed a class action on May 8, 2026, in the Circuit Court of Cass County, Missouri, against both Safe Fleet Holdings and parent company Clarience Technologies. The complaint pleads six causes of action: negligence, negligence per se under the Federal Trade Commission (FTC) Act and the Health Insurance Portability and Accountability Act (HIPAA) (a theory the defense could likely contest), breach of implied contract, invasion of privacy, unjust enrichment, and breach of fiduciary duty. Ferry himself experienced a fraudulent charge in February 2025 and spent $20 a month on credit monitoring afterward.
| Date | Event |
|---|---|
| April 13, 2024 | Intrusion and data theft |
| May 27, 2025 | Breach discovered (409 days later) |
| July 18, 2025 | Notification to class members |
| May 8, 2026 | Class action filed |
| July 30, 2026 | Preliminary settlement approval |
| November 2, 2026 | Final approval hearing |
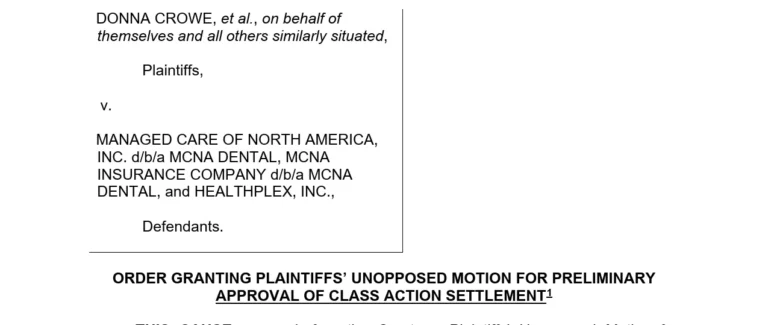
The docket shows a company that never planned to fight. Safe Fleet never filed an answer. Defense counsel appeared on June 8, 2026, filed an unopposed motion for preliminary approval 37 days later on July 15, and the court granted it July 30, giving the company a preliminary deal within 12 weeks of being sued. Either defense counsel at Mullen Coughlin told them the expected value of fighting was ugly, or the meter was simply running too fast to justify optimism. Both readings point the same direction.
The Settlement Bill
Safe Fleet agreed to settle this summer, and the settlement terms await final approval at a November 2 fairness hearing. The deal breaks into fixed and variable pieces. Fixed pieces are the plaintiffs’ attorneys’ fees, capped at $250,000, plus $2,000 service awards each for two class representatives, for $254,000 total. Variable pieces scale with participation, and the structure resembles most claims-made settlements in this space.
- Out-of-pocket losses up to $2,500 per claimant with documentation
- A flat $50 alternative payment requiring no documentation
- Two years of CyEx Financial Shield Complete credit monitoring with $1 million in fraud insurance, per enrollee
- Settlement administration costs, paid by the defendants
Estimating the variable side requires participation benchmarks, because claims-made settlements live or die on how many people bother to file. Morrison & Foerster’s data breach litigation year-in-review found most settlements drew claim rates around 1%, with outliers between 2% and 6%. Model a conservative 1% claim rate with a realistic mix of mostly flat $50 payments and a handful of documented losses, and claimant payments land somewhere between $3,700 and $190,000. Even the outlier participation rates only bend the top end of that range.
Credit monitoring is the bigger swing, and it swings on enrollment. Benchmark notification models assume roughly $30 per enrolled person per year, and employee classes tend to enroll at higher rates than consumer classes because contact data is clean and the offer lands in a company email people still read. Two years of coverage for 10% to 20% of a 7,478-person class runs roughly $45,000 to $90,000. Administration costs for a class this size typically run $100,000 to $150,000 in practice, though the notice doesn’t pin a number. Stack the fixed and variable pieces together, and the settlement component lands at about $400,000 to $680,000.
Add defense fees. Mullen Coughlin’s Carolyn Purwin Ryan joined local counsel Brett Carl Randol, and even a compressed 12-week engagement with zero contested motion practice bills real money. Comparable breach defense work runs $150,000 to $400,000 depending on how messy the pre-suit investigation was. This one involved more than a year of undetected intrusion followed by multi-state notification, so the messier end is plausible.
Then there’s the incident response itself, which happened a full year before anyone sued. A mid-market forensic investigation of this scope runs $50,000 to $80,000. Mailing, printing, and postage for 7,478 notifications runs $11,000 to $36,000 at standard per-record rates, while multi-state regulatory reporting to attorneys general in Maine, Massachusetts, New Hampshire, Texas, and Vermont, plus legal review of the notification letters, adds another $25,000 to $50,000. That response bucket totals $86,000 to $166,000.
| Category | Low Estimate | High Estimate |
|---|---|---|
| Settlement (fees, awards, claims, monitoring, admin) | $400,000 | $680,000 |
| Defense legal fees | $150,000 | $400,000 |
| Breach response and notification | $86,000 | $166,000 |
| Total | $640,000 | $1.25 million |
Against the IBM Cost of a Data Breach Report 2026, which studied 602 organizations between March 2025 and February 2026, Safe Fleet looks cheap. The global average breach cost hit a record $4.99 million, and the US average reached $11.5 million. Per-record costs in IBM’s series run about $160, which puts the model price for 7,478 stolen SSNs near $1.2 million. The reconstructed total of $640,000 to $1.25 million brackets that figure neatly, with the model price sitting near the top of the range.
Safe Fleet dodged the big-number tier only because the class was small. Same failure, applied to a customer database of 750,000 people instead of an HR folder of 7,478, scales to eight figures in a straight line. Nothing about their security posture protected them from that outcome. Their file count did.
What It Would Have Cost To Avoid This
The complaint faults Safe Fleet for inadequate technical safeguards, poor employee training, and generally deficient data security, which is what breach complaints always say. We don’t know the specific control that failed, because neither the company nor the courts have said. But the defensive menu that stops the overwhelming majority of breaches of this type is short and boring.
- Multi-factor authentication (MFA), at roughly $20 to $50 per user per year, or $38,000 to $95,000 annually across Safe Fleet’s roughly 1,900 current employees (the breach reached a larger 7,478-person pool because it swept in former staff)
- Security awareness training, at $10 to $30 per user per year, or $19,000 to $57,000
- Endpoint detection and response (EDR), at $50 to $150 per user per year, or $95,000 to $285,000
- Managed security monitoring, which small IT teams buy as a service, running roughly $200,000 to $600,000 annually
A defensible floor of MFA and awareness training runs about $57,000 to $152,000 a year at prevailing rates, with EDR and monitoring as the next tier up. That’s the annual subscription for not becoming a named defendant in Cass County.
The comparison doesn’t flatter Safe Fleet. One year of that floor package runs roughly a tenth of what the incident cost all-in at the midpoints, and the full outcome cost represents somewhere between four and 20 years of floor-package prevention spend, depending on which ends of the ranges you pick. IBM’s 2026 report found breaches contained inside 200 days averaged $4.32 million, while longer ones averaged $5.65 million, and detection speed tracks closely with monitoring spend. Safe Fleet’s intrusion sat undetected for 409 days, well beyond IBM’s 247-day mean for identifying and containing a breach end to end. Nobody was watching. The company that spends $100,000 a year on detection tools generally doesn’t need 15 months and an outside contractor to learn it’s been robbed.
The prevention math gets uglier still once you stack detection on top. A company that had bought monitoring wouldn’t just have spent less; it would have shrunk the damages window, cut the fraud exposure, and gutted the notification-delay argument that anchored the plaintiffs’ case.
Why This Case Matters
Two months before the intrusion, Oak Hill Capital closed the sale of Safe Fleet to Clarience Technologies, a Genstar-backed platform. Neither entity files public financials, so there’s no way to express the settlement as a share of annual profit. What’s measurable is the substitution metric, and it’s brutal. A breach that cost somewhere north of half a million dollars, potentially past a million, was offset by roughly $57,000 to $152,000 a year of controls that a reasonable insurer would have demanded anyway. Depending on where the final claims tally lands, Safe Fleet traded years of security budget against one avoidable incident, while eating reputational damage and regulator attention across five states. That’s a bad trade.
The timing deserves emphasis too. According to IBM’s 2026 report, one in four malicious breaches is now AI-enabled, averaging $6 million each, up 56% year over year. The floor under everyone’s downside is rising. Safe Fleet’s deal lands them in a market where their outcome gets more expensive with every report cycle, not less.
The Bottom Line
Safe Fleet’s projected numbers look almost modest by breach standards, assuming the deal survives its November final-approval hearing. And the cost structure that made this survivable for a mid-sized HR breach is the same structure that produces eight-figure disasters when the affected dataset grows. The executives who signed off on skipping MFA and skimping on monitoring weren’t avoiding security spend. They were deferring it, at interest, payable in Cass County.
The lesson isn’t buy more tools. It’s price your accepted risks honestly, because the plaintiffs’ bar and the actuaries already have.